From the Fortress
Field notes on data resilience, ransomware recovery, and what actually works when the alert fires.
-
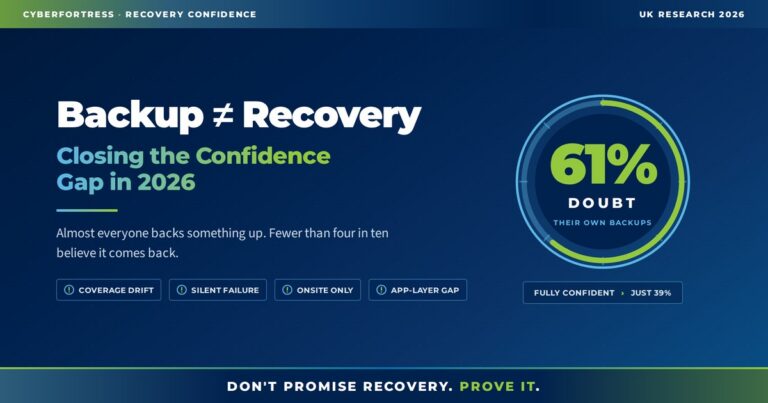
61% of Companies Don’t Trust Their Backups to Actually Restore. They’re Right Not To.
By Javi Cano • September 3, 2026Only 39% of UK businesses say they are fully confident they could recover their cloud data after a cyberattack. Backup adoption, meanwhile, is nearly universal. Almost everyone is backing something up. Fewer than four in ten believe it would actually come back. That gap has a name now: the recovery confidence gap. It is quietly… -
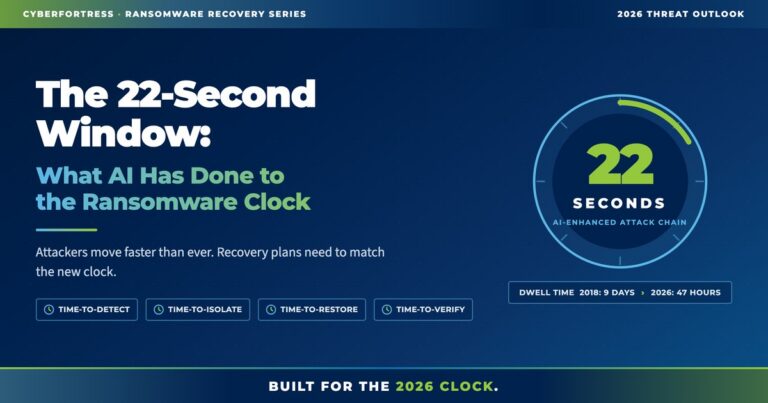
The 22-Second Window: What AI Has Done to the Ransomware Clock
By Javi Cano • August 12, 2026In 2018, ransomware attackers spent an average of nine days inside a network before encrypting. That was enough time to detect, respond, and recover. In 2026, that window collapsed to 47 hours on average, with some AI-enhanced attack chains measured in seconds. Recovery plans built for the slower clock no longer fit the math: businesses… -
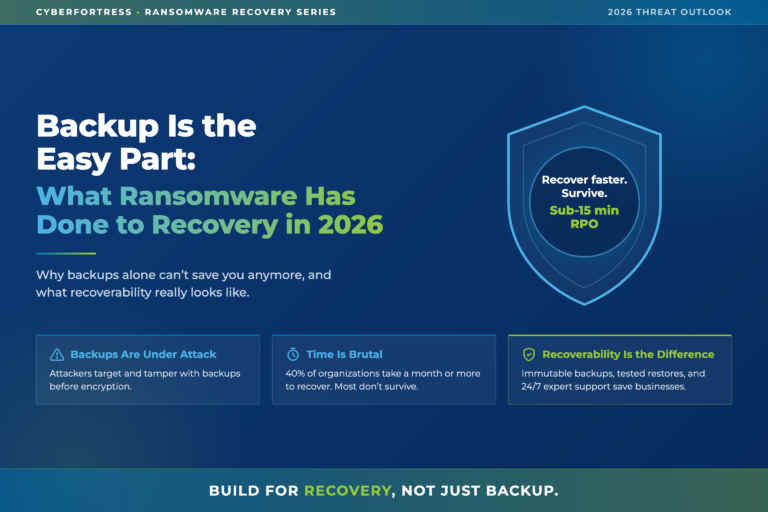
Backup Is the Easy Part: What Ransomware Has Done to Recovery in 2026
By Javi Cano • August 5, 2026In 2026, having backups is no longer the same as having recovery. Modern ransomware operators spend days inside a network locating and tampering with backup chains before encryption fires. An encryption fire means the restore most organizations plan to reach for is already compromised when they need it. The businesses that recover are the ones… -

Backups Won. The Attackers Stopped Caring.
By Javi Cano • July 23, 2026Roughly 97% of organizations with encrypted backups can now recover from a traditional ransomware attack without paying which is a genuine win for the backup industry. It may be safe to say that ransomware crews noticed, and pure data-exfiltration extortion is up 23% year over year as a result. Attackers skip encryption entirely, walk out… -
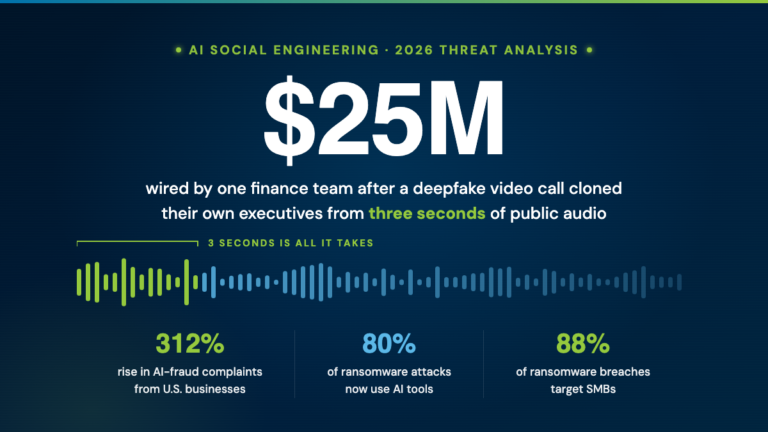
Three Seconds of Audio. One $25 Million Wire Transfer.
By Javi Cano • July 2, 2026AI voice clones and deepfake video calls now bypass the security awareness training most businesses rely on. The three defenses that actually work in 2026 are out-of-band verification procedures for high-stakes actions, 24/7 behavioral monitoring at the identity layer, and recovery readiness that assumes some attacks will succeed. Key Takeaways 3 seconds of audio. One… -
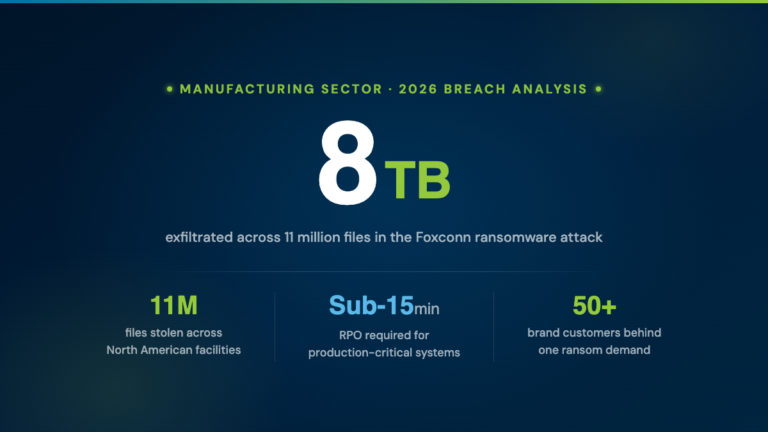
Foxconn Just Lost 8 Terabytes. Your Supply Chain Is Next.
By Javi Cano • July 1, 2026On May 12, 2026, ransomware crew Nitrogen breached Foxconn, exfiltrated 8TB across 11 million files, and disrupted production at multiple North American facilities. This ransomware attack exposed why contract manufacturers and their suppliers are now premium ransomware targets. The defenses that work are sub-15-minute recovery points, immutable air-gapped backups unreachable by stolen credentials, and rehearsed… -
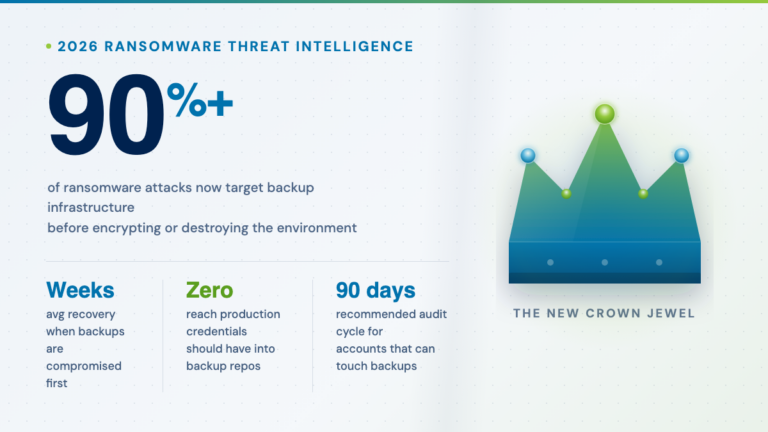
Your Backup Admin Is the New Crown Jewel. Attackers Already Know.
By Javi Cano • June 25, 2026More than 90% of modern ransomware attacks target backup infrastructure before encrypting production. They are destroying the recovery copy which removes the only exit that doesn’t involve paying the ransom. The architecture that survives this requires immutable storage the production environment cannot disable, identity and network isolation for the backup console, and geo-separated air-gapped recovery… -
Why a Data Recovery Lab Hired a Crisis Counselor
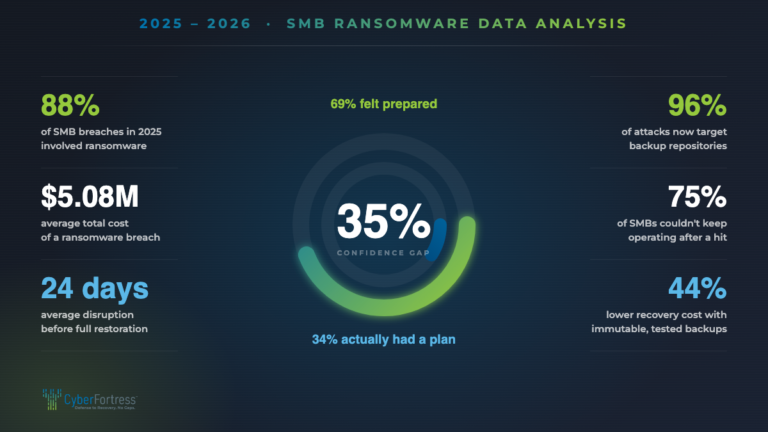
By Javi Cano • June 24, 2026SMBs are losing the 2026 ransomware war because 88% of SMB breaches now involve ransomware, 96% of attacks target backup repositories directly, and only 34% of SMBs have a formal incident response plan despite 69% believing they were well-prepared. The fix is treating protect, detect, and recover as one connected discipline rather than three separate… -
Your Hospital Wasn’t Breached. Your Billing Vendor Was. Same Result.
By Samantha Hottle • June 16, 2026In 2026, ransomware groups have shifted their primary entry point into healthcare from direct hospital attacks to third-party vendors like billing platforms, with healthcare ransomware up 36% year over year. Hospitals need independent backups of vendor-held data, monitoring at the vendor integration layer, and documented continuity plans for multi-day vendor outages, because a vendor breach… -
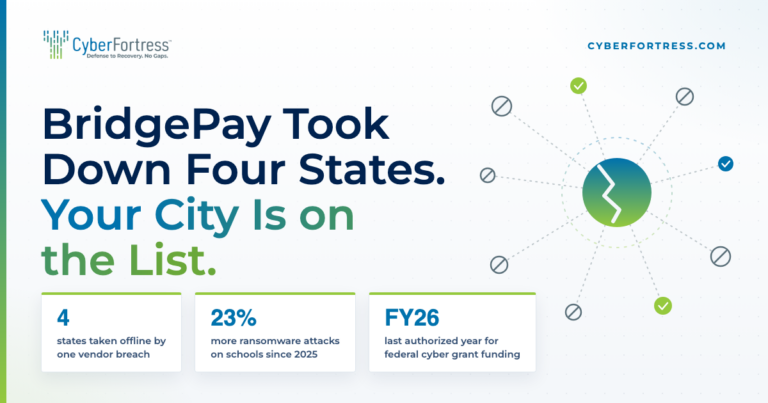
BridgePay Took Down Four States. Your City Is on the List.
By Samantha Hottle • June 11, 2026A ransomware attack on third-party payment processor BridgePay Network Solutions earlier this year took out credit-card payment systems for cities, utilities, and at least one county across four states. The municipalities themselves had not been breached. The processor had. Residents standing at the counter trying to pay their water bills did not care. That is… -
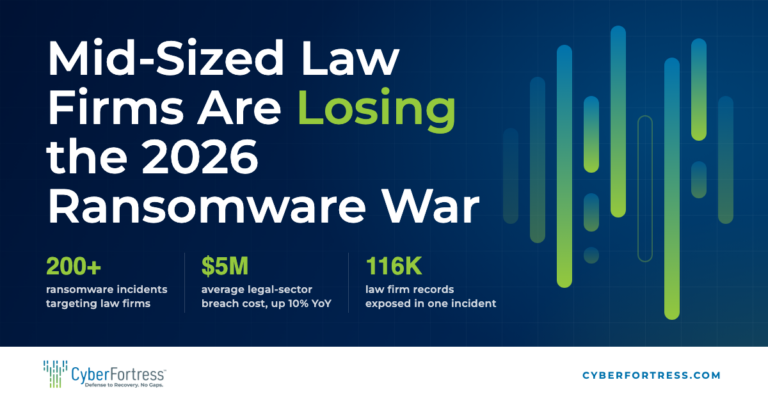
Mid-Sized Law Firms Are Losing the 2026 Ransomware War
By Javi Cano • June 11, 2026Mid-sized law firms are losing the 2026 ransomware war because attackers have shifted to breaching the concentrated legal-tech vendor stack (LexisNexis and DocketWise to name a few) and exposing thousands of firms at once, while most 20-to-300-attorney firms lack the security maturity to respond. Firms need independent SaaS backup, endpoint backup for remote attorneys, managed… -
When the EHR Goes Dark: Healthcare Recovery as a Patient Safety Decision
By Javi Cano • June 3, 2026Roughly 40% of healthcare organizations take a month or more to recover from a ransomware incident because modern attackers treat the backup repository as a primary target and tamper with recovery points before deploying ransomware. Patient-safe EHR recovery requires air-gapped immutable backups, monthly restore testing against ransomware scenarios, and a 24/7 escalation path. Treating recovery…