How to Pass Enterprise Backup Audits in 2026
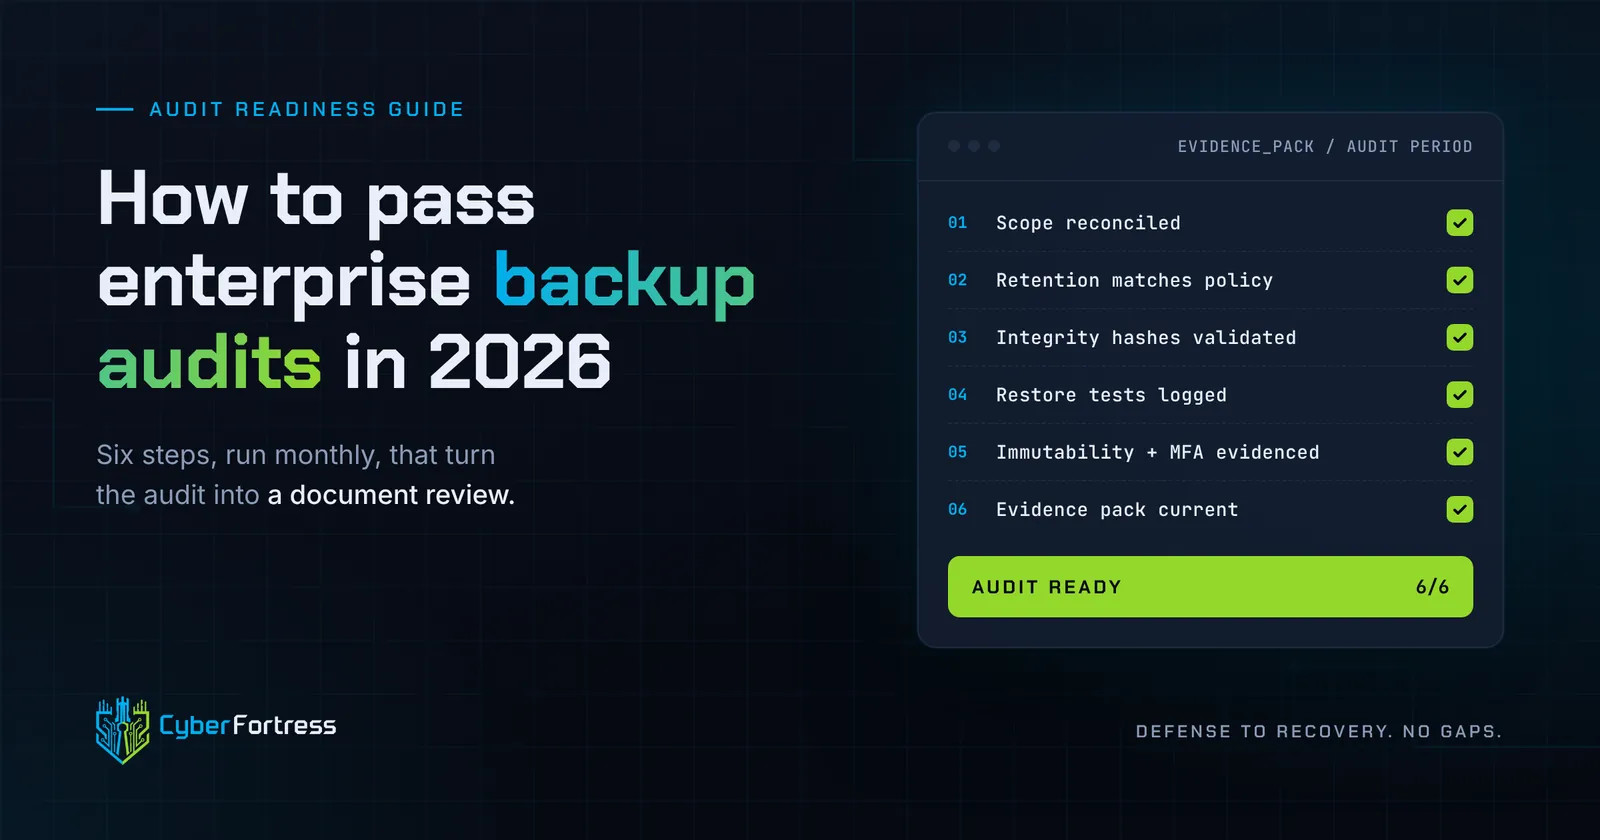
Work through six steps in order: reconcile scope against your asset inventory, prove data integrity, perform and document restore tests, evidence immutability and access control, then assemble a standing evidence pack. Do them monthly and the audit becomes a document review.
Step 1: Reconcile scope against the asset inventory
Export every system from your CMDB or asset register, export every protected workload from your backup platform, and compare the two. Investigate every difference.
Unprotected systems are the most common audit finding and the easiest to fix, and the reconciliation report is itself the evidence. Run it once and you will find something. Everyone does.
Step 2: Confirm retention matches written policy
Compare configured retention against your documented policy and against each applicable regulation. Check three specific things: retention length per data class, what happens when a source file is deleted, and whether anyone shortened retention during the period.
Configuration drift produces findings even when nothing was ever lost. Somebody trimmed retention to control a storage bill in March, yet the policy document still says seven years.
Step 3: Prove the data is intact
Enable continuous integrity checking on stored recovery points and keep the results. Backup integrity testing catches silent corruption that no job report will ever surface. Auditors accept hash validation logs far more readily than a success percentage.
Step 4: Test restores and write down the numbers
Run restores on a schedule and record the workload, the recovery point used, the start and finish times, who performed it, whether it met the RTO, and any problems encountered. Cover at least a single file, a full server or virtual machine, and one application-aware restore such as a database or mailbox.
Documented timings are the strongest evidence you can hold because they record what actually happened.
Step 5: Evidence immutability and access control
Produce the immutability mechanism and lock duration, the list of roles that can modify retention or delete data, proof of multi-factor authentication on the backup console, and access and deletion logs for the period.
Show explicitly that production administrators cannot delete backup data. That is the control an attacker tests first and an auditor tests hardest.
Step 6: Assemble a standing evidence pack
Keep one folder per audit period containing the scope reconciliation, retention export, integrity results, restore test log, immutability configuration, access logs, the disaster recovery plan with its last test date, and a named owner for backup operations. Update it monthly.
Teams that maintain this finish audits in days. Teams that do not spend weeks reconstructing a past nobody wrote down.
What do auditors ask that teams handle badly?
- “Show me a restore you performed in the audit period.” – Most teams have no log.
- “Which systems are not backed up?”- Most teams have never reconciled.
- “Can your administrators delete backups?” – The honest answer is often yes.
- “When did you last test the disaster recovery plan?” – Frequently, longer ago than the policy requires.
- “How do you know the data is not corrupt?” – Job success is offered. Integrity validation is not.
Frequently asked questions
How far in advance should we prepare? Preparation should be continuous. If you are starting cold, six to eight weeks is realistic to reconcile scope, run tests, and build the evidence pack.
Does a managed backup provider make audits easier? Usually. Scope reporting, verification results, and restore evidence are produced as part of the service. Confirm you receive them in a format you can hand to an auditor.
Next step
CyberFortress runs the reconciliation, the verification, and the restore tests, then delivers the evidence pack. Start with the questions auditors ask.
Test Your Fortress · Prove Your Recovery
Related reading: Data backup and disaster recovery FAQs
A backup you have never restored is a guess. Trinity turns it into proof.
Seven questions show where your recovery plan stands today. Or skip ahead and talk to a CyberFortress recovery specialist about your environment.
More from the Fortress
-
Whose Database Is Your Data In?
FulcrumSec published roughly 8.8 million people’s data from Manchester Airports Group over the first weekend of September 2026,…
-
Managed Server Backup RPO and Recovery Times in 2026
For a 200-person company in 2026, a reasonable managed server backup posture is a 15-minute to 4-hour RPO…
-
Outsourcing Server Backups in 2026 Full Guide
Outsourcing server backups works when the contract covers monitoring, remediation, verified restore testing, immutable offsite storage, and assisted…
-
You Can’t Out-Patch an Attacker That Adapts in 31 Seconds
Researchers have documented what they are calling JadePuffer: a ransomware operation reportedly run end-to-end by an autonomous LLM…