DATA PROTECTION TRENDS, NEWS & BACKUP TIPS
The 22-Second Window: What AI Has Done to the Ransomware Clock
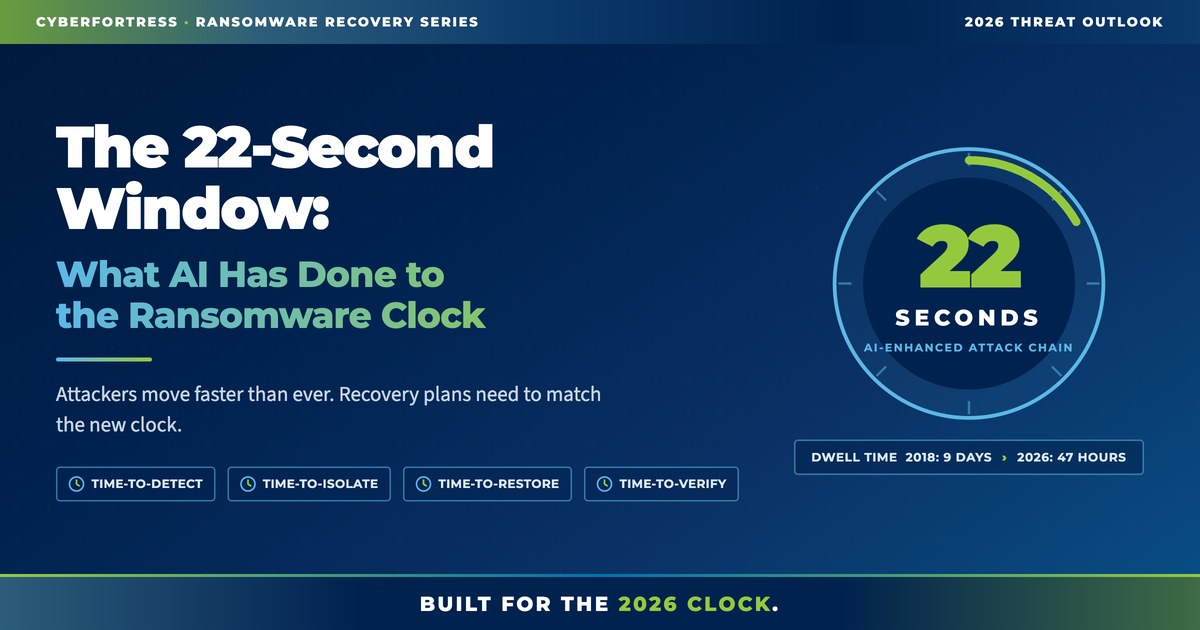
In 2018, ransomware attackers spent an average of nine days inside a network before encrypting. That was enough time to detect, respond, and recover. In 2026, that window collapsed to 47 hours on average, with some AI-enhanced attack chains measured in seconds. Recovery plans built for the slower clock no longer fit the math: businesses that survive need sub-minute detection, immutable recovery copies the attacker cannot reach, and restore processes rehearsed against an adversary. Not just a hardware failure.
Key Takeaways
- Average attacker dwell time has dropped from nine days in 2018 to roughly 47 hours in 2026; some AI-enhanced attack chains move from initial access to encryption in seconds
- CISA’s Q1 2026 reporting puts AI-enhanced ransomware success rates 73% above traditional variants and the gap is widening month over month
- Recovery time is not one number – it is four sequential clocks: time-to-detect, time-to-isolate, time-to-restore, and time-to-verify; most plans only model the third
- Time-to-verify which is confirming restored data is clean and the attacker is no longer resident. This is the clock most organizations skip, and the one that produces quiet repeat attacks
- Three architectural requirements that match the 2026 clock: RPOs measured in minutes (not hours), immutable geo-separated recovery copies unreachable from production credentials, and restore drills that simulate adversarial conditions
When the Attacker Is Faster Than the Recovery Plan
In 2018, the average ransomware attacker spent about nine days inside a victim’s network before deploying encryption. There was time. Time to investigate an alert. Time to call a vendor. Time to convene an incident response meeting and weigh options.
In 2026, that window has collapsed to roughly 47 hours on average, and in some attack chains the time from initial access to encryption can be measured in seconds. CISA’s Q1 2026 reporting puts the success rate of AI-enhanced ransomware 73% above traditional variants, and the gap is widening month over month.
For most IT and security leaders, that statistic doesn’t land emotionally because it is hard to picture. Picture this instead. A 22-second attack chain means the person who clicked the phishing link is still reading the next email by the time their organization has been encrypted.
Recovery plans built for the older clock no longer fit the math.
The Recovery Clock Has Four Hands
A useful way to think about ransomware recovery in 2026 is as four distinct clocks running in sequence, not as one number called “recovery time.”
- Time-to-detect. The interval between the attacker entering the environment and the defender becoming aware of it. Compressed dwell times have shrunk this clock the most. Detection that depended on weekly scans or business-hours triage was already insufficient by 2024. By 2026, it is entirely out of phase with the threat.
- Time-to-isolate. The interval between detection and the moment the affected systems stop spreading or exfiltrating data. This clock measures whether the response team has the authority and the technical means to act in minutes rather than meetings.
- Time-to-restore. The interval between isolation and the moment the business has working systems again. This is the clock most organizations have measured for years, and the one most heavily affected by whether the recovery copy is reachable, intact, and tested.
- Time-to-verify. The interval between restoration and the moment the team can confirm the restored data is clean, the attacker is not still resident in the environment, and the operational posture is safe to resume. This is the clock that gets skipped in real incidents, and the one that produces the quiet repeat attacks.
Adding those four numbers together produces the real-world recovery time the business actually experiences, and the aggregate is what most plans fail to model.
What the New Numbers Demand
If detection happens within minutes and the recovery clock is measured in days, the math is unkind. An organization with weekly restore tests and 24-hour RPOs is operating at a tempo the attacker can outrun without any AI assistance at all. The AI-enabled attacker mainly makes the problem visible to more victims, sooner.
Three architectural decisions follow from the new clock.
- The RPO has to shrink. Recovery point objectives measured in 24 hours or longer mean a day of business data is gone every time. In environments handling transactions, patient records, or production telemetry, that loss is no longer acceptable. RPOs measured in minutes are now achievable, and they have become the bar for any business that runs critical operations on its data.
- The recovery copy has to be unreachable. A backup that lives on the same network as production, uses the same identity provider, and gets touched by the same administrative accounts is something an attacker who compromised one credential can erase. Immutable, write-once-read-many storage in a geo-separated, identity-isolated vault has become the baseline answer for any business that takes the new clock seriously.
- The recovery process has to be rehearsed against an adversary, not an outage. A restore that has only ever been tested as a hardware failure scenario does not capture the conditions that appear in 2026: corrupted recent snapshots, contaminated identity infrastructure, time pressure measured in hours. Drills that resemble the real threat are the only drills that produce reliable recovery estimates.
Where CyberFortress Fits in the New Clock
CyberFortress was built around recoverability in environments that cannot afford the older numbers. LiveVault delivers sub-15-minute RPO targets with immutable retention and AES 256-bit encryption. Managed BaaS and DRaaS handle the operational rhythm of the recovery process: monthly verification, tested restore paths, and 24/7 U.S.-based recovery specialists on call. The Trinity Platform brings that recovery capability together with managed detection and response, so the time-to-detect and time-to-restore clocks are coordinated by a single team rather than handed off across vendors.
The shift that matters here is integration. Each clock improves marginally on its own, while the clocks compound when they are managed together as one operating discipline.
A Practical Audit for Your Recovery Clock
If you have not measured your own recovery clock against 2026 numbers, three exercises are worth running this quarter.
- Pick a critical system and write down the actual time from incident declaration to a verified, clean operational restore in your environment. The number that shows up in a real drill, not the number on the slide deck.
- Decompose that number into the four clocks above. Note which one is the largest, and what would have to be true to cut it in half.
- Compare your time-to-detect against your time-to-encrypt assumption. If the attacker is faster than the detection, the recovery copy and the recovery process are doing work the prevention layer can no longer do alone.
The numbers from those exercises will tell you whether your current architecture survives the 2026 clock, or simply hasn’t been tested against it yet. Both answers are useful, and the second is the more dangerous of the two.
Frequently Asked Questions
How fast do ransomware attacks move in 2026?
Average attacker dwell time has dropped from nine days in 2018 to roughly 47 hours in 2026, and AI-enhanced attack chains have compressed some incidents to seconds between initial access and encryption. CISA’s Q1 2026 reporting puts the success rate of AI-enhanced ransomware 73% above traditional variants, with the gap continuing to widen. Recovery plans built around the previous timeline shows weekly restore tests, 24-hour RPOs, business-hours detection that are now operating at a tempo the attacker can outrun without difficulty.
What are the four clocks of ransomware recovery?
Ransomware recovery time is best understood as four sequential clocks, not one number. Time-to-detect is the interval between the attacker entering the environment and the defender becoming aware. Time-to-isolate is the interval between detection and stopping the spread. Time-to-restore is the interval between isolation and working systems. Time-to-verify is the interval between restoration and confirmed confidence that the data is clean and the attacker is no longer present. Most organizations only plan for the third clock which is why real-world recovery times are much longer than the numbers estimated.
What is RPO and what should it be for a business in 2026?
RPO (Recovery Point Objective) is the maximum amount of data a business can afford to lose. It is measured as the time between the last clean backup and the moment of an attack. A 24-hour RPO means up to a full day of transactions, records, or operational data is unrecoverable every time. In 2026, for any business running critical operations on its data, RPOs measured in minutes have become the standard. LiveVault delivers sub-15-minute RPO targets with immutable, AES 256-bit encrypted retention.
Why is “time-to-verify” the most dangerous clock to skip?
Time-to-verify is the step that confirms the restored environment is clean. It is the moment that confirms that backup data is uncontaminated, the attacker is no longer resident, and the operational posture is safe to resume. Organizations that skip this step and return to operations too quickly are the source of most quiet repeat attacks, where the same attacker re-encrypts a business weeks after the first payment. A verified clean restore, not just a functional one, is the correct definition of recovery in 2026.
How does immutable backup protect against AI-enhanced ransomware?
AI-enhanced ransomware moves faster and more deliberately than earlier variants, often locating and destroying backup copies before encryption fires. Immutable, write-once-read-many storage in a geo-separated, identity-isolated vault removes that attack path. The recovery copy cannot be altered or deleted even if the attacker escalates to administrative credentials inside the production environment. The vault lives outside the production trust domain, so no credential the attacker harvests gives them access to it.
What does it mean to rehearse a restore against an adversary rather than an outage?
Most restore drills simulate a hardware failure: systems go offline, backup is pulled, systems come back. An adversarial restore drill simulates 2026 conditions: recent snapshots are corrupted during the dwell period, identity infrastructure is contaminated, and the team is working under hours of time pressure rather than days. The adversarial drill reveals which restore points are actually trustworthy, how long verification takes under realistic conditions, and whether the recovery process can be executed by the people available at 2 a.m. on a weekend.
CyberFortress provides managed cyber resilience built around the 2026 recovery clock — sub-15-minute RPO, immutable geo-separated storage, and 24/7 U.S.-based recovery specialists coordinating all four clocks under one team. Contact us to measure your current recovery clock against the numbers that matter.