88% of Ransomware Victims Go Bankrupt. Is Your Business Next?
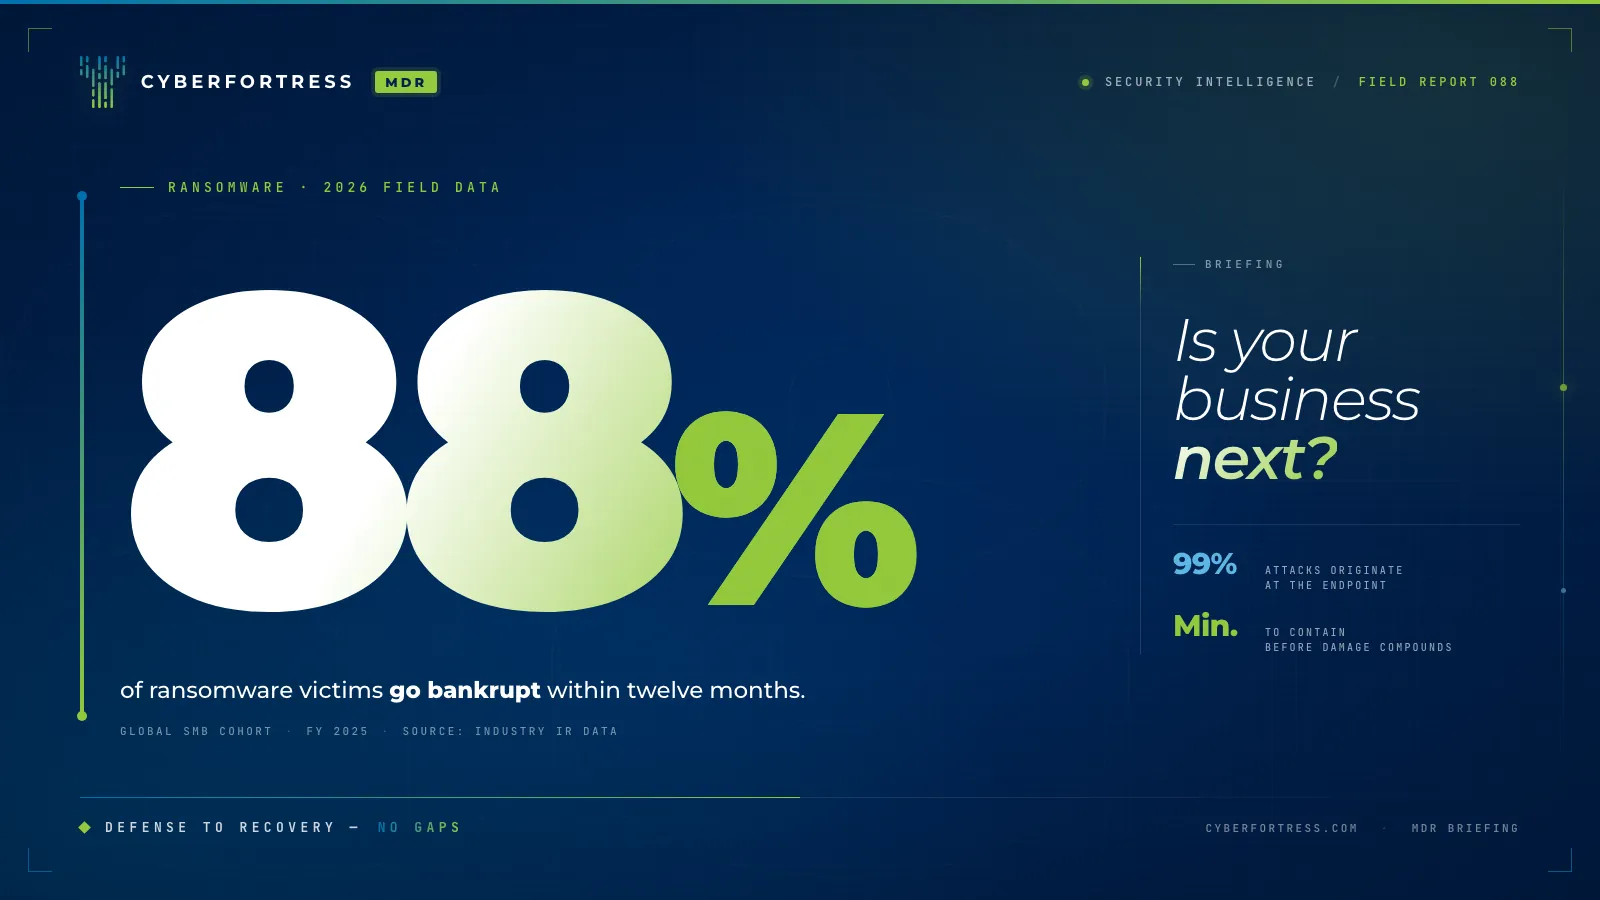
88% of businesses hit by ransomware go bankrupt within twelve months, and 99% of attacks start at the endpoint rather than the perimeter. Survival depends on closing the gap between security tools and recovery tools, because detection without recovery leaves you watching the fire, and recovery without detection restores a backup the attacker already seeded.
Key Takeaways
- 88% of businesses hit by ransomware go bankrupt within twelve months, and the cause is rarely that the attack was unstoppable. It is that the gap between security tooling and recovery tooling was wide enough to drive a truck through.
- 99% of malware payloads and data exfiltration happen at the endpoint, not the perimeter firewall or the cloud environment.
- Attackers dwell for weeks before detonating. In the scenario this post walks through, the payload maps the network, locates the backup server, and finds the Microsoft 365 data before firing at 2:47 AM on a Saturday.
- Every dollar spent on prevention saves roughly ten on recovery, and every hour of proactive hardening saves weeks of incident response.
- Detection without recovery means seeing the fire with no extinguisher, and recovery without detection means restoring from a backup the attacker deliberately seeded so the payload survives the restore.
- CyberFortress SaaS Backup and Recovery covers Exchange, SharePoint, OneDrive, and Teams with granular recovery down to a single email, restoration in under 15 minutes, and HIPAA, SOC II, and PCI-DSS compliance, protecting over 20,000 businesses and 200 million Microsoft 365 users.
Three Weeks Inside Before Anyone Noticed
It starts with one email.
Your accountant opens an invoice. The attachment looks legitimate. One click, and a piece of code embeds itself silently in the operating system. For the next three weeks, it watches. It maps your network. It finds your backup server. It finds your Microsoft 365 data. It finds everything.
Then, at 2:47 AM on a Saturday, it detonates.
Your files are encrypted. Your systems are offline. Your phone is ringing. And somewhere, a criminal is waiting for you to pay.
That’s not hyperbole. It’s the statistic that should keep every business owner and IT leader awake at night:
Read that first number again. 88%. Nearly nine out of ten businesses hit by ransomware are gone within twelve months.
Not because the attack was unstoppable. Because they weren’t ready for it. Because their defenses were fragmented. Because when the moment came, the gap between their security tools and their recovery tools was just wide enough for a criminal to drive a truck through.
That gap is what kills companies.
Your Endpoint Is the Front Line. Are You Protecting It?
99% of malware payloads and data exfiltration happen at the endpoint. Not the perimeter firewall. Not the cloud environment. the endpoint — your employee’s laptop, the remote worker’s home computer, the shared machine in the break room, each one needing endpoint backup and recovery
Attackers know this. They build entire campaigns around exploiting endpoint vulnerabilities. A phishing email, a malicious download, a compromised credential — that’s all it takes to get a foothold. And once they’re in, your clock starts ticking.
This is the problem with the old model of cybersecurity: it assumes the perimeter will hold. Deploy a firewall, install antivirus, call it done. But the perimeter hasn’t held for a decade. The question isn’t whether attackers will get in. The question is what happens when they do.
And the honest answer for most businesses is: nothing good.
Prevention Is Cheaper Than Recovery. By a Factor of Ten.
Every dollar spent on prevention saves roughly ten on recovery. Every hour of proactive hardening saves weeks of incident response. And yet, most organizations treat prevention as a checklist — something you do once at onboarding, then forget about until the auditor shows up.
That’s how companies end up on the losing side of the 88%.
Modern prevention isn’t a firewall and a quarterly password reset. It’s a living posture that shrinks your attack surface faster than attackers can grow it. The vulnerabilities criminals scan for on Monday need to be closed by Tuesday. The credentials stolen in last week’s third-party breach need to be useless by the time they’re tried against your login page. The phishing email that lands in your CFO’s inbox needs to fail the moment it’s clicked.
That means continuous patching and configuration enforcement, zero-trust access controls that assume every user and device is hostile until proven otherwise, and phishing-resistant authentication that neutralizes the single click most breaches depend on. It also means hardening the human layer — because your employees are the front line whether you’ve trained them or not.
The organizations that survive ransomware don’t just detect and recover faster. They give attackers fewer places to land in the first place.
Detection Isn’t Enough. But Neither Is Backup.
Here’s the trap most organizations fall into: they buy endpoint detection and response (EDR) tools, pat themselves on the back, and assume they’re protected. Or they invest heavily in backup, figure they can just restore if something goes wrong, and move on.
Both strategies are incomplete. And the gap between them is where companies die.
Detection without recovery means you can see the fire, but you have no extinguisher.
Recovery without detection means you restore from a backup that’s already infected.
That second scenario is more common than you’d think. Attackers deliberately seed ransomware into backup systems, waiting for their payload to survive a restore, which is why immutable backup with clean data verification matters. You think you’re recovering. You’re actually restarting the clock.
One Partner. Prevent, Detection, Containment, AND Recovery. No Gaps.
This is exactly the problem CyberFortress was built to solve.
CyberFortress MDR, doesn’t just monitor your endpoints — it actively hunts for threats, shrinks your detection window from months to minutes, and integrates directly with the recovery layer so that when something is found, the path to clean restoration is already in place.
The Trinity Platform — CyberFortress’s unified command center — ties all three pillars together under a single portal. Your IT team and C-suite get a live Risk Score and Recovery Readiness Score. Not a theoretical framework. Not a four-step plan collecting dust. A real, tested, verified assessment of your ability to survive an attack — updated in real time.
Wait — What About Your SaaS Data?
Here’s something most people don’t realize: protecting your data in the cloud is your job, not the platform’s. The infrastructure is covered. Your emails, your files, your Teams chats — that’s on you.
CyberFortress SaaS Backup and Recovery closes that gap entirely.. Automated cloud-to-cloud backups across Exchange, SharePoint, OneDrive, and Teams. Granular recovery down to a single email. Restoration in under 15 minutes. And full compliance with HIPAA, SOC II, and PCI-DSS.
Over 20,000 businesses and 200 million Microsoft 365 users are protected. Are you?
You Don’t Know When. But It’s Coming.
Here’s the uncomfortable truth: you are not too small to be targeted. You are not too obscure to be noticed. Ransomware gangs use automated scanning tools that probe millions of IP addresses every day. If you have a vulnerability, they will find it.
The only question is whether you’ll be ready when they do.
- Prevention alone isn’t enough — determined attackers will eventually find a way through.
- Detection without recovery is incomplete.
- Recovery without detection is dangerous.
- Gaps between any of the three are how companies die.
CyberFortress covers all three. One partner. One contract. One integrated strategy. Defense to Recovery — No Gaps.
Frequently Asked Questions
What percentage of businesses go bankrupt after a ransomware attack? 88% of businesses hit by ransomware are gone within twelve months. The cause is usually not that the attack was unstoppable, but that defenses were fragmented and the gap between security tools and recovery tools was wide enough for an attacker to exploit.
Where do most ransomware attacks actually begin? 99% of malware payloads and data exfiltration happen at the endpoint rather than the perimeter firewall or the cloud environment. That means employee laptops, remote workers’ home computers, and shared machines are the front line, and a phishing email or compromised credential is all it takes to establish a foothold.
How long do attackers stay in a network before deploying ransomware? Typically weeks. During that dwell time the code maps the network, locates the backup server, and identifies cloud data such as Microsoft 365 before detonating, which is usually timed for nights or weekends when response is slowest.
Is backup alone enough to protect against ransomware? No. Recovery without detection risks restoring from a backup the attacker deliberately seeded, meaning the payload survives the restore and the clock restarts. Detection without recovery is equally incomplete, because seeing the attack does not restore operations.
Is prevention or recovery the better cybersecurity investment? Both are required, though every dollar spent on prevention saves roughly ten on recovery, and every hour of proactive hardening saves weeks of incident response. Prevention should be a living posture with continuous patching, zero-trust access controls, and phishing-resistant authentication rather than a checklist completed at onboarding.
Does Microsoft 365 back up my email and files automatically? Protecting data in the cloud is the customer’s responsibility, while the platform covers the infrastructure. Emails, files, and Teams chats need an independent backup, which CyberFortress provides across Exchange, SharePoint, OneDrive, and Teams with granular recovery down to a single email and restoration in under 15 minutes.
CyberFortress provides prevention, detection, and recovery under one accountable team so no gap exists for an attacker to exploit. Contact us to find out which side of the 88% your current architecture puts you on.
A backup you have never restored is a guess. Trinity turns it into proof.
Seven questions show where your recovery plan stands today. Or skip ahead and talk to a CyberFortress recovery specialist about your environment.
More from the Fortress
-
Whose Database Is Your Data In?
FulcrumSec published roughly 8.8 million people’s data from Manchester Airports Group over the first weekend of September 2026,…
-
Managed Server Backup RPO and Recovery Times in 2026
For a 200-person company in 2026, a reasonable managed server backup posture is a 15-minute to 4-hour RPO…
-
Outsourcing Server Backups in 2026 Full Guide
Outsourcing server backups works when the contract covers monitoring, remediation, verified restore testing, immutable offsite storage, and assisted…
-
You Can’t Out-Patch an Attacker That Adapts in 31 Seconds
Researchers have documented what they are calling JadePuffer: a ransomware operation reportedly run end-to-end by an autonomous LLM…